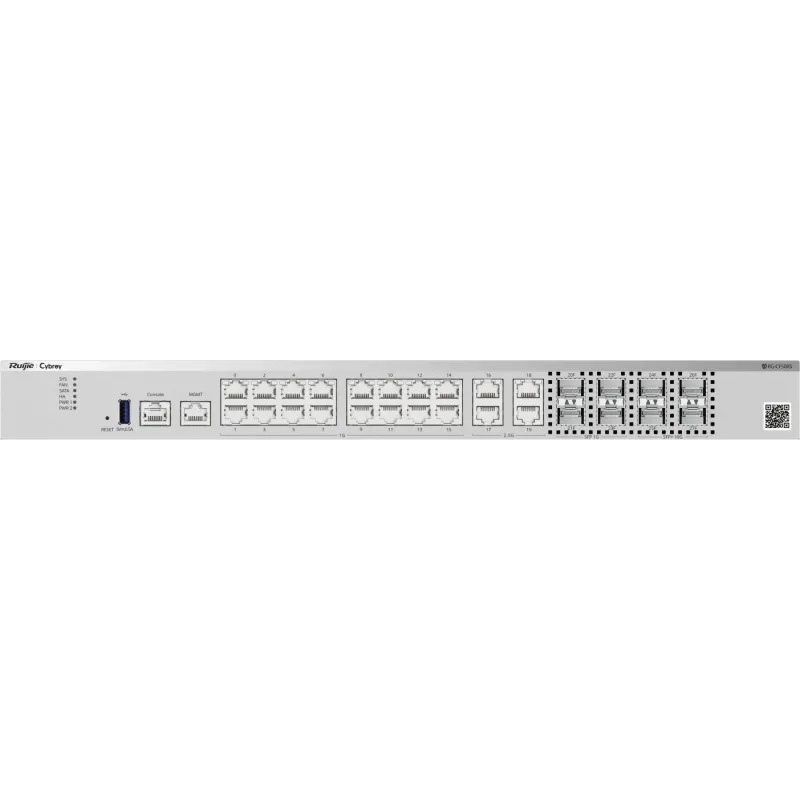
Ruijie Cybrey RG-CF50S Datasheet
Ruijie Cybrey RG-CF Series Next-Generation High-Performance Firewalls Hardware Installation and Reference Guide
Ruijie Cybrey RG-CF series next-generation high-performance firewalls NGFW_NTOS 1.0R13 User Manual
RG-CF50XS Ruijie Cybrey Next-Generation Firewall พร้อม IPS, WAF, AI Security และ 10G SFP+
RG-CF50XS เป็น Next-Generation High-Performance Firewall (NGFW) จาก Ruijie Cybrey สำหรับป้องกันภัยคุกคามและบริหารความปลอดภัยของระบบเครือข่ายองค์กร ออกแบบสำหรับติดตั้งบริเวณ Internet Gateway, Network Security Boundary, Data Center Boundary และระบบเครือข่ายสาขา เหมาะกับสำนักงาน โรงแรม โรงพยาบาล สถานศึกษา โรงงาน และธุรกิจที่ต้องการตรวจสอบ Traffic พร้อมควบคุมการเข้าถึงระบบเครือข่าย
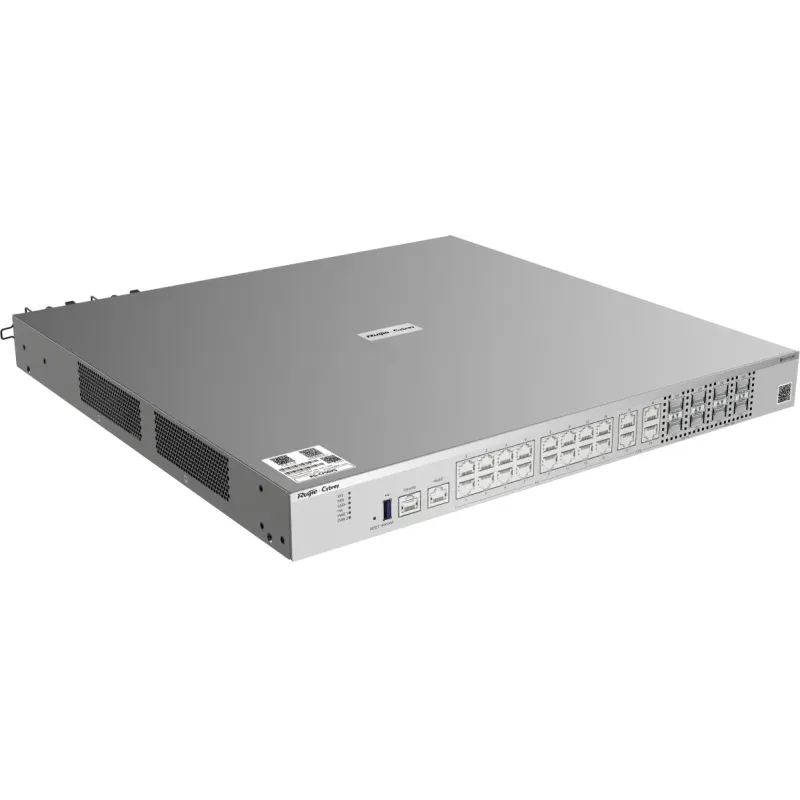
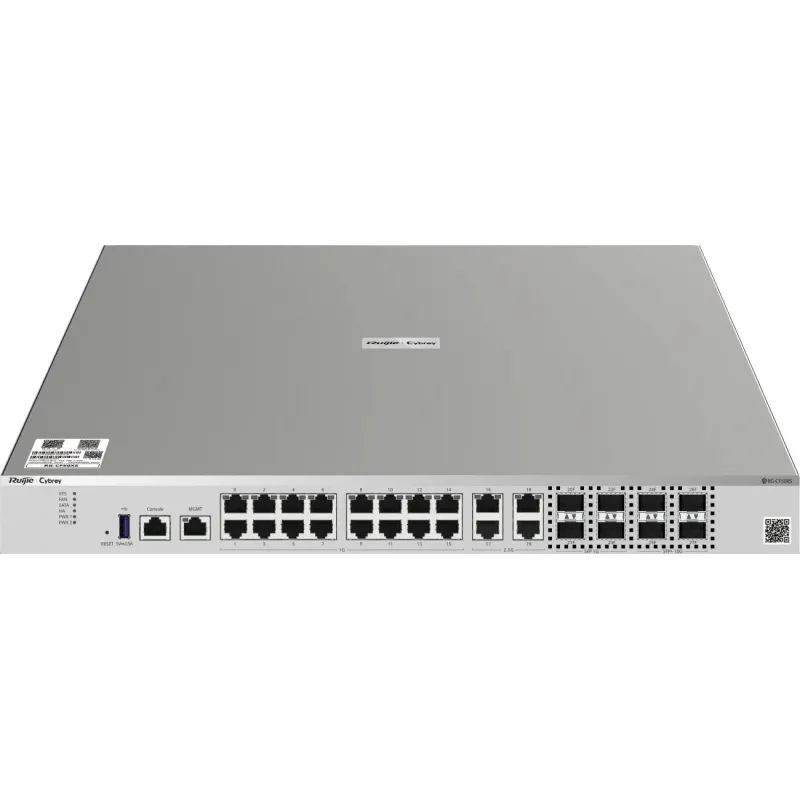
ตัวเครื่องรองรับ Firewall Throughput 14-17Gbps, IPS Throughput 3.5-4Gbps, NGFW Throughput 3.1-3.6Gbps และ Threat Protection Throughput 2.5-3Gbps ตาม Performance License ที่ติดตั้ง พร้อมพอร์ต Network รวม 28 พอร์ต ได้แก่ 16 Gigabit RJ45, 4 พอร์ต 2.5G RJ45, 4 Gigabit SFP และ 4 พอร์ต 10G SFP+
รองรับฟีเจอร์ Security ได้แก่ Intrusion Prevention System (IPS), Antivirus (AV), Web Application Firewall (WAF), Threat Intelligence, Application Control, URL Filtering และ AI Threat Detection โดยสามารถจัดการ Security Policy และตรวจสอบเหตุการณ์ผ่านระบบ Cloud Management ทั้งนี้การใช้งาน Security Features ต้องพิจารณา Security License ที่เกี่ยวข้อง
ข้อควรทราบ: RG-CF50XS Chassis ไม่มี Power Module ติดตั้งมาให้ ต้องซื้อ RG-PA150IB-F อย่างน้อย 1 ชุดก่อนใช้งาน และหากต้องการ All-in-One Security Features ต้องจัดหา Security License เพิ่มเติมตามรูปแบบการใช้งาน
Firewall Throughput 14-17Gbps พร้อม Threat Protection สูงสุด 3Gbps
RG-CF50XS ใช้ Hardware Platform สำหรับการรับส่งข้อมูลและตรวจสอบภัยคุกคาม โดยรองรับการขยายประสิทธิภาพผ่าน RG-CF50XS-500M-LIC Performance License ตามเงื่อนไขของผู้ผลิต
- Firewall Throughput: 14-17Gbps
- IPS Throughput: 3.5-4Gbps
- NGFW Throughput: 3.1-3.6Gbps
- Threat Protection Throughput: 2.5-3Gbps
- SSL Inspection Throughput: 1.2Gbps
- Concurrent TCP Sessions: สูงสุด 3,000,000 Sessions
- New TCP Sessions: สูงสุด 170,000 Sessions/Second
- Firewall Policies: สูงสุด 10,000 Policies
สำหรับ RG-CF50XS Chassis ประสิทธิภาพ Threat Protection เริ่มต้นที่ 2.5Gbps และสามารถขยายเป็น 3Gbps ด้วย RG-CF50XS-500M-LIC จำนวน 1 License โดยค่าประสิทธิภาพด้าน IPS, NGFW และ Threat Protection เป็นค่าที่วัดภายใต้การเปิดใช้งาน Security Features ตามเงื่อนไขของผู้ผลิต
Firewall Throughput เป็นค่าประสิทธิภาพการส่งต่อข้อมูลของ Hardware โดยใช้ UDP Packet ขนาด 1518 Bytes ส่วน Threat Protection Throughput เป็นค่าการรับส่งข้อมูลเมื่อเปิด Firewall, IPS, Application Control และ Malware Protection จึงควรใช้ Threat Protection Throughput เป็นข้อมูลหลักประกอบการเลือก Firewall สำหรับงานที่ต้องตรวจสอบภัยคุกคาม
Intrusion Prevention System (IPS) สำหรับตรวจจับและป้องกันการโจมตี
RG-CF50XS รองรับ Intrusion Prevention System (IPS) สำหรับตรวจสอบ Traffic และป้องกันการโจมตีตาม Security Signature โดยสามารถกำหนด IPS Template ตามระดับความรุนแรง ประเภทภัยคุกคาม Protocol และ Security Rules ที่ต้องการ
ผู้ดูแลระบบสามารถเลือกใช้ IPS Template ที่กำหนดไว้ล่วงหน้า ปรับแต่งกฎการตรวจจับ และกำหนดรายการยกเว้นสำหรับ Traffic ที่ต้องการอนุญาตตาม Security Policy ขององค์กร
เหมาะสำหรับการป้องกันระบบ Server, Network Services และเครือข่ายภายในจาก Traffic ที่มีรูปแบบเข้าข่ายการโจมตีตามฐานข้อมูล IPS ที่รองรับ โดยการใช้งานระบบ IPS ต้องพิจารณา Security License และการอัปเดต Signature Library
Antivirus, Threat Intelligence และ AI Threat Detection
RG-CF50XS รองรับ Antivirus (AV) สำหรับตรวจสอบภัยคุกคามจาก Malware โดยสามารถกำหนด Virus Protection Template แบบ Quick Scan หรือ Deep Scan และปรับแต่งการตรวจสอบตาม Protocol, Traffic Direction และรายการยกเว้นได้
รองรับ Threat Intelligence สำหรับตรวจสอบข้อมูลภัยคุกคามและช่วยระบุการเชื่อมต่อที่มีความเสี่ยง โดย Datasheet ระบุการทำงานร่วมกับฐานข้อมูลจาก Google และ Kaspersky พร้อมการกำหนด Threat Intelligence Policy และ Exclusion List
นอกจากนี้ยังรองรับ AI Threat Detection สำหรับวิเคราะห์พฤติกรรมการโจมตีและ Traffic ที่ผิดปกติ รวมถึงภัยคุกคามที่มีการเปลี่ยนรูปแบบการโจมตีหรือใช้พฤติกรรมที่ตรวจจับได้ยาก โดยใช้การวิเคราะห์พฤติกรรมและข้อมูลประกอบจากระบบ Cloud AI
- Antivirus: รองรับ Quick Scan และ Deep Scan
- Threat Intelligence: รองรับฐานข้อมูลภัยคุกคามและ Custom Threat Intelligence
- AI Threat Detection: ตรวจสอบพฤติกรรมผิดปกติและการโจมตีที่ซับซ้อน
- Signature Updates: รองรับ Local, Online และ Automatic Signature Library Upgrade
Web Application Firewall (WAF) และการป้องกัน Web Services
RG-CF50XS รองรับ Web Application Firewall (WAF) สำหรับกำหนดนโยบายตรวจสอบและป้องกันภัยคุกคามที่มุ่งโจมตี Web Application โดยสามารถใช้ WAF Template ร่วมกับ Security Policy ของ Firewall
เหมาะสำหรับระบบที่มี Web Server หรือ Web Application ให้บริการผ่านเครือข่าย เช่น ระบบเว็บไซต์องค์กรและบริการภายในที่เปิดให้เข้าถึงผ่าน Network Boundary โดยต้องออกแบบ Security Policy ให้สอดคล้องกับรูปแบบ Traffic ของระบบ
การใช้งาน WAF ต้องตรวจสอบ All-in-One Security License และเงื่อนไขของบริการที่รองรับก่อนติดตั้งจริง
Application Control, URL Filtering และ DNS Protection
RG-CF50XS รองรับ Application Control สำหรับจำแนกและกำหนดนโยบายควบคุม Traffic ตามประเภท Application และ Application Group ช่วยให้ผู้ดูแลระบบสามารถกำหนดสิทธิ์การเข้าถึงบริการและควบคุมการใช้งาน Internet ตามความต้องการขององค์กร
รองรับ URL Filtering, URL Safe Search, Keyword Filtering และ File Filtering สำหรับกำหนดนโยบายการเข้าถึงเว็บไซต์ เนื้อหา และประเภทไฟล์ รวมถึง DNS Filtering และ DNS Safe Search สำหรับเพิ่มการควบคุมการใช้งาน Internet
- Application Control: กำหนด Policy ตาม Application และ Application Group
- URL Filtering: ควบคุมการเข้าถึงเว็บไซต์ตามนโยบาย
- Keyword Filtering: กรองเนื้อหาตาม Keyword
- File Filtering: กำหนดนโยบายตามประเภทไฟล์
- DNS Protection: DNS Filtering และ DNS Safe Search
- Traffic Control: กำหนดนโยบายควบคุม Traffic ตาม Template
DoS/DDoS Defense และ Network Attack Protection
RG-CF50XS รองรับการป้องกัน DoS/DDoS Attack ผ่านระบบ Security Defense ของ Firewall พร้อมฟังก์ชัน Local Defense สำหรับกำหนดนโยบายป้องกันการโจมตีที่มุ่งเป้าไปยังอุปกรณ์และบริการเครือข่าย
ผู้ผลิตระบุว่ามี Hardware Component สำหรับช่วยป้องกัน DoS/DDoS Attack ภายใน CPU โดยสามารถทำงานร่วมกับ Security Policy เพื่อเพิ่มการป้องกัน Traffic ที่ผิดปกติ
รองรับ ARP Attack Defense สำหรับป้องกัน ARP Spoofing และ ARP Flooding รวมถึงการกำหนด Global Blocklist และ Allowlist เพื่อควบคุม Traffic หรือการเชื่อมต่อที่ต้องการบล็อกหรืออนุญาต
SSL Inspection และ SSL Proxy สำหรับตรวจสอบ Encrypted Traffic
RG-CF50XS รองรับ SSL Inspection Throughput สูงสุด 1.2Gbps พร้อม SSL Proxy Policy สำหรับกำหนดเงื่อนไขการตรวจสอบ Traffic ที่เข้ารหัสตาม Objects, Content และ Security Zones
รองรับการจัดการ SSL Proxy Certificates ทั้งการเพิ่ม นำเข้า ลบ ตรวจสอบ และดาวน์โหลด Certificate รวมถึงการตั้งค่า Global SSL Proxy Certificate และ Domain/Application Allowlist
ฟังก์ชัน SSL Proxy เหมาะสำหรับองค์กรที่ต้องการตรวจสอบ Traffic ที่เข้ารหัสตามนโยบายความปลอดภัย โดยควรออกแบบการใช้งาน Certificate และข้อยกเว้นให้สอดคล้องกับระบบ Client และบริการที่ใช้งานจริง
Port Scan และ Traffic Learning สำหรับสร้าง Firewall Policy
RG-CF50XS มีฟีเจอร์ Port Scan สำหรับตรวจสอบ IP Address และ Port ของระบบ Server พร้อม Traffic Learning สำหรับเรียนรู้ความสัมพันธ์ของการเข้าถึงบริการภายในเครือข่ายจาก Traffic ที่เกิดขึ้นจริง
ผู้ดูแลระบบสามารถนำข้อมูลจาก Port Scan และ Traffic Learning มาประกอบการสร้าง Access Control Policy เพื่อกำหนดว่า Client หรือระบบใดควรเข้าถึง Server ผ่าน Port ใดได้บ้าง ช่วยลดขั้นตอนการสำรวจ Service และการกำหนด Firewall Rules ในช่วงเริ่มติดตั้ง
- Port Scan: ตรวจสอบ IP Range และ Service Ports
- Traffic Learning: บันทึก Destination IP, Port และ Traffic ผิดปกติ
- Policy Creation: รองรับการสร้าง Access Control Policy จากข้อมูลที่ตรวจพบ
- Traffic Learning Logs: รองรับการ Export Logs
Policy Simulation สำหรับตรวจสอบผลก่อนปรับ Firewall Rules
RG-CF50XS รองรับ Policy Simulation Space สำหรับทดลองเพิ่ม ลบ หรือแก้ไข Security Policy และนำกฎที่ปรับเปลี่ยนมาเปรียบเทียบกับ Traffic ที่เกิดขึ้นจริง เพื่อประเมินความแตกต่างของการจับคู่ Policy ก่อนนำการตั้งค่าไปใช้งาน
เหมาะสำหรับระบบที่มี Firewall Rules จำนวนมาก หรือมี Service สำคัญที่ต้องควบคุมการเข้าถึงอย่างละเอียด ช่วยให้ผู้ดูแลระบบประเมินผลกระทบของการเปลี่ยนแปลงและลดความเสี่ยงจากการกำหนด Policy ผิดพลาด
Intelligent Service Diagnostic Center และ Packet Tracing
RG-CF50XS รองรับ Intelligent Service Diagnostic Center สำหรับช่วยวิเคราะห์ปัญหาการเชื่อมต่อระหว่าง Client และ Target Resources โดยแสดงข้อมูล Fault และคำแนะนำสำหรับตรวจสอบสาเหตุ
ฟังก์ชัน Packet Tracing สามารถใช้ติดตามการประมวลผล Packet ผ่าน Security Service Modules ภายในอุปกรณ์ เพื่อช่วยตรวจสอบว่า Traffic ผ่านหรือถูกจัดการโดย Policy ส่วนใดของ Firewall
รองรับ Device Health Diagnosis และ One-click Fault Information Collection สำหรับเก็บข้อมูลประกอบการวิเคราะห์ปัญหาของระบบ Network และ Security
Multi-WAN Load Balancing, Policy-based Routing และ NAT
RG-CF50XS รองรับการกำหนด Interface เป็น LAN หรือ WAN โดย WAN สามารถใช้ PPPoE, DHCP หรือ Static IP และสามารถกำหนด Interface Mode แบบ Routing, Transparent หรือ Bypass ตามรูปแบบการติดตั้ง
รองรับ IPv4/IPv6 Static และ Dynamic Routing, Policy-based Routing (PBR), ISP Address Library-based Routing, Application-based Routing และ Egress Load Balancing สำหรับกำหนดเส้นทาง Traffic ผ่าน Internet Link ที่ต้องการ
รองรับ Multi-WAN Load Balancing และ WAN Failover สำหรับระบบที่ใช้ Internet มากกว่าหนึ่งเส้น โดยสามารถนำไปออกแบบเส้นทาง Internet หลักและเส้นทางสำรองร่วมกับ Security Policy ขององค์กร
มีฟังก์ชัน NAT, NAT Policy, Server Port Mapping, NAT Address Pool Status และ Aggregate Interface รวมถึง VLAN Subinterface สำหรับแยกเครือข่ายตาม VLAN ID
IPsec VPN, SSL VPN และ SD-WAN สำหรับเชื่อมต่อสาขา
RG-CF50XS รองรับ VPN หลายประเภท ได้แก่ IPsec VPN, SSL VPN, PPTP VPN และ L2TP VPN สำหรับเชื่อมต่อเครือข่ายระหว่างสถานที่และรองรับการเข้าถึงระบบจากภายนอกตามรูปแบบ VPN ที่กำหนด
- IPsec VPN Throughput: สูงสุด 10Gbps
- Gateway-to-Gateway IPsec VPN Tunnels: สูงสุด 1,000 Tunnels
- SSL VPN Throughput: สูงสุด 2.2Gbps
- Concurrent SSL VPN Users: Recommended Maximum 2,125 Users ใน Tunnel Mode
- SD-WAN Performance: สูงสุด 2.4Gbps
- Maximum SD-WAN Tunnels: 4,000 Tunnels
- Maximum SD-WAN Branches: 1,000 Branches
รองรับ SD-WAN Integration ร่วมกับ Cloud Platform สำหรับบริหารและตรวจสอบการเชื่อมต่อหลายสาขาจากส่วนกลาง เหมาะสำหรับสำนักงานที่ต้องการใช้ Firewall เป็นส่วนหนึ่งของระบบรักษาความปลอดภัยและการเชื่อมต่อระหว่างสาขา
28 Service Ports พร้อม Gigabit, 2.5G RJ45 และ 10G SFP+
RG-CF50XS มี Network Service Ports รวม 28 พอร์ต รองรับการเชื่อมต่อผ่าน Gigabit Ethernet, Multi-Gigabit Ethernet และ Fiber Optic เพื่อใช้เป็น Internet Gateway หรือ Network Security Boundary ตามโครงสร้างเครือข่ายองค์กร
- Gigabit RJ45: 16 x 10/100/1000BASE-T
- Multi-Gigabit RJ45: 4 x 10/100/1000/2.5GBASE-T
- Gigabit SFP: 4 x 1GE SFP
- 10G SFP+: 4 x 10GE SFP+
- Management: 1 x RJ45 MGMT
- Console: 1 x RJ45 Console (RS-232)
- USB: 1 x USB 3.0
สามารถนำพอร์ต Network มากำหนด Security Zones และออกแบบการเชื่อมต่อระหว่าง Internet, LAN, Server และ DMZ ได้ตามความสามารถของระบบ โดย Optical Transceiver ต้องเลือกให้เข้ากันได้กับพอร์ตและความเร็วที่ใช้งาน
64GB eMMC พร้อมช่องติดตั้ง SSD/HDD สำหรับ Session Logs
RG-CF50XS มี Built-in Storage ขนาด 64GB eMMC พร้อมช่องติดตั้ง 2.5-inch SATA Hard Disk จำนวน 1 ช่อง สำหรับเพิ่มความสามารถในการจัดเก็บ Session Logs และ Local Reports
รองรับ Storage Expansion Modules ตามรายการของผู้ผลิต ได้แก่ RG-NSEC-SSD-480G-B-M ขนาด 480GB และ RG-NSEC-HDD-1T-B ขนาด 1TB โดย Storage Module ต้องจัดหาแยกจากตัวเครื่อง
ข้อควรทราบ: การใช้งาน Session Logs และ Reports ภายในตัวอุปกรณ์ต้องติดตั้ง Hard Disk เพิ่มเติม แม้ตัวเครื่องจะมี Built-in 64GB eMMC อยู่แล้ว โดยผู้ผลิตกำหนดให้ใช้ Storage Module จาก Ruijie เพื่อความเข้ากันได้และความเสถียรของระบบ
Cloud Management, Security Reports และ Network Monitoring
RG-CF50XS รองรับ Unified Cloud Management สำหรับบริหารอุปกรณ์และ Security Policy จากส่วนกลาง พร้อมการซิงโครไนซ์ข้อมูลขึ้น Cloud เพื่อใช้ในการวิเคราะห์และสร้างรายงานด้าน Network และ Security
รองรับ Remote Monitoring, Batch Configuration, Automatic Inspection, Configuration Backup และ System Upgrade พร้อม SNMPv1/v2c/v3 และ Open API สำหรับเชื่อมต่อกับระบบบริหารจัดการอื่นที่รองรับ
ระบบ Monitoring รองรับการแสดง Security Status และ Network Operation Status พร้อม Logs หลายประเภท เช่น Security Log, Content Filtering Log, System Log, VPN Log และ HA Log โดย Session Logs และ Local Reports ต้องมี Hard Disk ตามข้อกำหนดของผู้ผลิต
รองรับ Redundant Power Supply พร้อม Hot-Swappable Power Modules
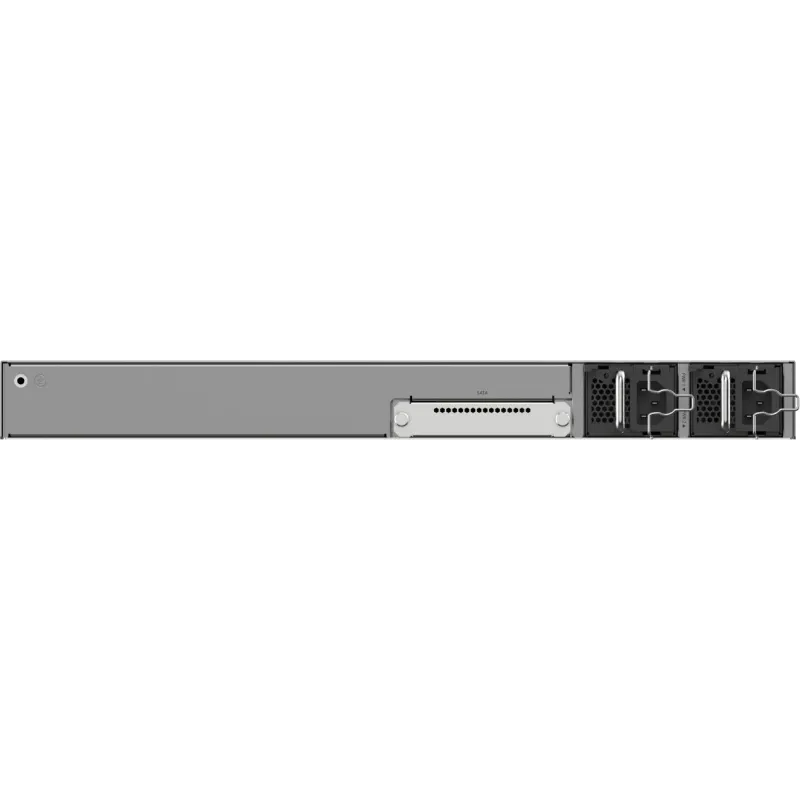
RG-CF50XS มีช่องติดตั้ง Power Module จำนวน 2 ช่อง รองรับ Power Module รุ่น RG-PA150IB-F ขนาด 150W ซึ่งสามารถใช้เป็นแหล่งจ่ายไฟหลักและติดตั้งเพิ่มเติมสำหรับ Power Redundancy
เมื่อมี Power Module 2 ชุดทำงานร่วมกันเพื่อรองรับ Redundancy สามารถถอดเปลี่ยน Power Module หนึ่งชุดระหว่างที่อีกชุดยังจ่ายไฟให้กับอุปกรณ์ได้ตามเงื่อนไขของผู้ผลิต
- Power Module: RG-PA150IB-F ขนาด 150W
- Power Module Slots: 2 ช่อง
- AC Input: 100-240V AC, 50/60Hz
- HVDC Input: 190-290V DC ตาม Specification ของ Power Module
- Power Redundancy: รองรับเมื่อใช้ Power Module 2 ชุด
- Hot-Swappable: รองรับการเปลี่ยน Power Module ตามเงื่อนไข Redundancy
- Maximum Power Consumption: 90W
ข้อควรทราบ: RG-CF50XS Chassis ไม่มี Power Module ติดตั้งมาให้ ต้องซื้อ RG-PA150IB-F อย่างน้อย 1 ชุดก่อนใช้งาน และต้องซื้อชุดที่สองเพิ่มเติมหากต้องการ Power Redundancy
Rack Mount 1U สำหรับติดตั้งในห้อง Network และ Data Center
RG-CF50XS ออกแบบสำหรับติดตั้งในตู้ Rack มาตรฐาน 19 นิ้ว ขนาด 1U โดยตัวเครื่องมีขนาด 442 x 420 x 43.6 มม. น้ำหนัก 5 กก. พร้อมพัดลมระบายความร้อนภายในจำนวน 2 ตัว
รองรับอุณหภูมิการทำงาน 0°C ถึง 45°C ที่ระดับความสูงต่ำกว่า 1,800 เมตร และความชื้นสัมพัทธ์ 10-90% RH แบบ Non-condensing เหมาะสำหรับติดตั้งภายในห้อง Network หรือ Data Center ที่มีระบบระบายความร้อนเหมาะสม
เหมาะสำหรับ Internet Gateway, DMZ และ Network Security Boundary
RG-CF50XS เหมาะสำหรับติดตั้งเป็น Firewall ที่ Internet Gateway เพื่อควบคุมการเชื่อมต่อเข้าออกขององค์กร และใช้บริเวณ Security Boundary เพื่อแยกการเข้าถึงระหว่างเครือข่ายภายในกับระบบ Server หรือ DMZ
สามารถนำไปใช้กับสำนักงาน โรงแรม โรงพยาบาล สถานศึกษา โรงงาน และองค์กรที่มีเครือข่ายหลายสาขา โดยเลือกใช้งาน IPS, WAF, Antivirus, Threat Intelligence, VPN และ SD-WAN ตามความต้องการด้านความปลอดภัยและ Security License ที่ติดตั้ง
ก่อนเลือกซื้อควรพิจารณา Threat Protection Throughput, ประเภท Security License, จำนวน Network Ports, VPN Capacity และความต้องการจัดเก็บ Logs รวมถึง Power Module ที่ต้องซื้อแยก เพื่อให้ Firewall รองรับการใช้งานจริงของระบบเครือข่ายได้เหมาะสม
Product Specifications
| Product Information |
| Model | RG-CF50XS |
| Brand | Ruijie Cybrey |
| Product Series | RG-CF50XS Series |
| Product Type | Next-Generation High-Performance Firewall (NGFW) |
| Recommended Use | Internet Gateway, Network Security Boundary, Data Center Boundary, DMZ และเครือข่ายสาขาของสำนักงาน โรงแรม โรงพยาบาล สถานศึกษา โรงงาน และองค์กรที่ต้องการ IPS, WAF, VPN และ Cloud Management |
| Firewall Performance and Capacity |
| Firewall Throughput | 14-17Gbps (1518-byte IPv4 UDP Packets) |
| IPS Throughput | 3.5-4Gbps |
| NGFW Throughput | 3.1-3.6Gbps |
| Threat Protection Throughput | 2.5Gbps (Chassis) / 3Gbps เมื่อเพิ่ม RG-CF50XS-500M-LIC จำนวน 1 License |
| SSL Inspection Throughput | 1.2Gbps |
| Concurrent Sessions | 3,000,000 TCP Sessions |
| New Sessions per Second | 170,000 TCP Sessions/Second |
| Firewall Policies | 10,000 Policies |
| Performance Expansion | RG-CF50XS-500M-LIC เพิ่ม Threat Protection Throughput 500Mbps ต่อ License ตาม Ordering Information |
| Performance Test Conditions | NGFW วัดเมื่อเปิด Firewall, IPS และ Application Control; Threat Protection วัดเมื่อเปิด Firewall, IPS, Application Control และ Malware Protection |
| Port Specifications |
| Gigabit RJ45 Ports | 16 x 10/100/1000BASE-T |
| 2.5G RJ45 Ports | 4 x 10/100/1000/2.5GBASE-T |
| Gigabit SFP Ports | 4 x 1GE SFP |
| 10G SFP+ Ports | 4 x 10GE SFP+ |
| Total Service Ports | 28 Ports (16 Gigabit RJ45 + 4 Multi-Gigabit RJ45 + 4 SFP + 4 SFP+) |
| Management Port | 1 x RJ45 MGMT |
| Console Port | 1 x RJ45 Console (RS-232) |
| USB Port | 1 x USB 3.0 |
| 4G Cellular Port | ไม่รองรับ |
| Security Features |
| Firewall Protection | Stateful Firewall Policy, Security Zones, Access Control และ Local Defense ตามความสามารถของระบบ |
| Intrusion Prevention (IPS) | IPS Templates, Signature-based Detection, Custom Rules และ Exclusion Rules |
| Antivirus (AV) | Quick Scan, Deep Scan, Protocol/Direction-based AV Templates และ Virus Exclusions |
| Web Application Firewall | WAF Template สำหรับกำหนดนโยบายตรวจสอบและป้องกัน Web Application |
| Threat Intelligence | รองรับ Threat Intelligence, Custom Threat Intelligence และ Threat Exclusions โดย Datasheet ระบุ Google และ Kaspersky |
| AI Threat Detection | AI-powered Stealthy Attack และ Abnormal Behavior Detection |
| Application Control | Application และ Application Group Policy |
| Content Filtering | URL Filtering, URL Safe Search, Keyword Filtering และ File Type Filtering |
| DNS Protection | DNS Filtering และ DNS Safe Search |
| DoS/DDoS Defense | รองรับ DoS/DDoS Attack Defense Policies และ Hardware-based Defense Component |
| ARP Attack Defense | ARP Spoofing และ ARP Flooding Defense |
| Blocklist / Allowlist | Global Blocklist และ Allowlist |
| SSL Proxy | SSL Proxy Policy, Certificate Management และ Domain/Application Allowlists |
| User Authentication | User Management, Authentication Server และ Authentication Policy Configuration |
| Security License and Expansion |
| All-in-One Security License | IPS + AV + TI-G + TI-K + URL Filtering + Application Control + AI + WAF |
| 1-Year Security License | RG-CF50XS-UTP-LIS-1Y |
| 1-Month Security License | RG-CF50XS-UTP-LIS-1M |
| Performance License | RG-CF50XS-500M-LIC |
| License Bundle Options | มี Bundle แบบ 2.5G และ 3G พร้อม Security License ระยะเวลา 1, 3 หรือ 5 ปี ตาม Ordering Information |
| License Included in Chassis | Datasheet ไม่ระบุว่ามี All-in-One Security License รวมอยู่ใน RG-CF50XS Chassis; ต้องเลือกซื้อ License หรือ Bundle ตามรายการสั่งซื้อ |
| Router and Network Features |
| Interface Modes | Routing, Transparent และ Bypass Mode |
| WAN Connection | PPPoE, DHCP และ Static IP |
| VLAN | VLAN Subinterfaces และ VLAN ID Configuration |
| Security Zones | รองรับการกำหนด Security Zone Objects |
| Routing | IPv4/IPv6 Static และ Dynamic Routing ตาม Software Specifications |
| Policy-based Routing | PBR, ISP Address Library-based Routing และ Application-based Routing |
| Multi-WAN | Egress Load Balancing, Multi-WAN Load Balancing และ WAN Failover |
| NAT | NAT Policies, NAT Address Pool, Batch Import, ALG และ Server Port Mapping |
| DHCP | DHCP Server และ DHCP Relay |
| DDNS | รองรับ DDNS Service Providers หลายรายการตาม Software Specifications |
| High Availability | Active/Standby Automatic Switchover และ VRRP |
| VPN and SD-WAN |
| VPN Protocols | IPsec VPN, SSL VPN, PPTP VPN และ L2TP VPN |
| IPsec VPN Throughput | 10Gbps |
| Gateway-to-Gateway IPsec Tunnels | 1,000 Tunnels |
| SSL VPN Throughput | 2.2Gbps |
| Concurrent SSL VPN Users | Recommended Maximum 2,125 Users (Tunnel Mode) |
| SD-WAN Performance | 2.4Gbps |
| Maximum SD-WAN Tunnels | 4,000 Tunnels |
| Maximum SD-WAN Branches | 1,000 Branches |
| Management and Diagnostics |
| Cloud Management | รองรับ Unified Cloud Management, Remote Monitoring และ Log Upload to Cloud |
| Management Protocols | SNMPv1/v2c/v3 |
| Policy Management | Intelligent Policy Manager, Traffic Learning และ Policy Simulation Space |
| Port Scan | รองรับ Port Scan และการนำผลการตรวจสอบมาช่วยสร้าง Security Policy |
| Diagnostic Tools | Fault Analysis, Packet Tracing, Device Self-Test และ One-click Fault Collection |
| Cloud Features | Batch Configuration, Automatic Inspection, Cloud Data Synchronization และ Security Reporting |
| System Maintenance | Configuration Backup/Restore, System Upgrade/Rollback และ Signature Library Updates |
| API Integration | Open APIs สำหรับเชื่อมต่อ Third-party Platforms |
| Storage and Logs |
| Built-in Storage | 64GB eMMC |
| Hard Disk Slot | 1 x 2.5-inch SATA Slot |
| Supported SSD | RG-NSEC-SSD-480G-B-M, 480GB (ซื้อแยก) |
| Supported HDD | RG-NSEC-HDD-1T-B, 1TB (ซื้อแยก) |
| Hard Disk Hot Swapping | ไม่รองรับสำหรับ Storage Modules ที่ระบุ |
| Session Logs and Local Reports | ต้องติดตั้ง Hard Disk เพิ่มเติมตามข้อกำหนดของผู้ผลิต |
| Cloud Reporting | รองรับ Cloud Data Synchronization สำหรับ Analysis และ Reporting |
| Power Supply |
| Power Module Slots | 2 x Power Module Slots |
| Power Module Included | ไม่มี Power Module ใน Chassis ต้องซื้อแยกอย่างน้อย 1 ชุด |
| Supported Power Module | RG-PA150IB-F (150W) |
| Power Input | 100-240V AC, 50/60Hz; Power Module รองรับ 190-290V HVDC ตาม Specification |
| Power Redundancy | รองรับเมื่อใช้ Power Module 2 ชุด |
| Power Module Hot Swapping | รองรับภายใต้เงื่อนไขที่มี Power Module สำรองจ่ายไฟอยู่ |
| Maximum Power Consumption | 90W |
| Physical and Environment |
| Form Factor | Rack Mount 1U, Standard 19-inch Rack |
| Dimensions | 442 x 420 x 43.6 mm |
| Weight | 5 kg |
| Cooling Fan | 2 x Built-in Fixed Fans |
| Operating Temperature | 0°C ถึง 45°C ที่ระดับความสูงต่ำกว่า 1,800 เมตร |
| Operating Humidity | 10% RH ถึง 90% RH, Non-condensing |
| Operating Altitude | 0-5,000 เมตร โดยช่วงอุณหภูมิที่ระบุมีเงื่อนไขตามระดับความสูง |
| Safety Standard | IEC 62368-1:2014 |
| RoHS | Yes |
| Package Contents |
| Items in Package | RG-CF50XS Chassis x 1, Grounding Wire x 1, Rubber Pads x 4, L-shaped Rack-mount Brackets x 2, M4 x 8mm Screws x 10, Rear Mounting Brackets x 2, Guide Rails x 2, Warranty Card x 1 และ User Manual x 1 |
| Required Accessories | Power Module RG-PA150IB-F อย่างน้อย 1 ชุด ต้องซื้อแยก |
| Optional Accessories | Power Module ชุดที่ 2, All-in-One Security License, Performance License, Ruijie SSD/HDD และ SFP/SFP+ Optical Transceivers ที่รองรับ ตามการใช้งาน |
| Warranty |
| Warranty | รับประกันศูนย์ Ruijie Cybrey Thailand 3 ปี |